Introduction
Netcat (nc) Explained: The Swiss Army Knife of Networking is a description of one of the easiest but most versatile command line utilities used for network communication and testing. Netcat (nc) is used to establish TCP connections, send UDP traffic, listen on ports, transfer data, test services, and troubleshoot connectivity difficulties.
Netcat (nc) is a common tool for Linux and Unix-like systems, although equivalent implementations exist for other operating systems as well. Its command-line interface is excellent for networking novices in training, as well as administrators and security specialists doing authorised testing.
According to the OpenBSD literature, nc is a utility for opening TCP connections, transmitting UDP packets, listening on ports, and port scanning.
What Is Netcat?
Netcat ( nc ) is a command-line program for reading and writing directly across network connections . Instead of a huge graphical interface, it offers users simple commands for making connections and moving data across endpoints.
Netcat (nc) can be both server and client. One system could be waiting to be connected to, while the other system connects to it.
For example:
nc -l 1234
This is a simple Netcat listener on port 1234. Another machine can connect by using:
nc 192.168.1.10 1234
Once connected, text typed in at one end can be read at the other end. This simple behaviour shows how sockets and client-server communication works.
How Netcat Works In Networking?
Netcat (nc) functions by communicating with network sockets. Sockets are the endpoint for sending or receiving data across a network by applications.
In TCP the protocol is connection-oriented which implies that the client tries to establish a connection with the target service. With UDP, you can send data without creating the same type of connection.
Netcat (nc) supports both TCP and UDP communication. OpenBSD’s implementation uses the -u option for UDP.
A simple TCP connection looks like:
nc example.com:80
You could try a UDP connection with:
nc -u example.com 53
The exact settings may differ between Netcat implementations, thus users should consult their local nc -h or man page.
Common Netcat Commands
Netcat (nc) has some useful settings for networking.
Make a Netcat Listener
To make a simple listener:
nc -l 5000 # start a listener on port 5000
The -l option makes the tool operate in listen mode.
Test a TCP Port
Netcat (nc) can be used for Netcat port testing.
nc -zv example.com 443
If your implementation supports these options, -v will give verbose output and -z will scan the port without providing any application data.
Perform Port Scanning
Netcat (nc) can do simple Netcat port scanning:
nc -zv 192.168.1.10 20-30
The -z option to inspect listening ports is documented in the OpenBSD man page.
Use only scan systems that you own or have authorised authority to test.
Netcat TCP And UDP Examples
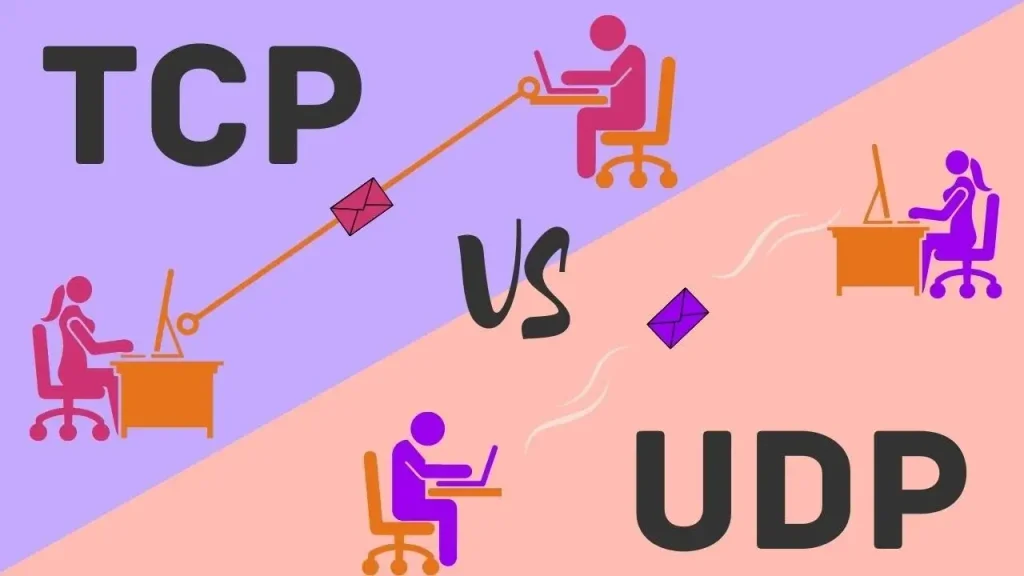
Netcat (nc) is a tool that lets you grasp the difference between TCP and UDP easily.
For a TCP server:
nc -l 9000
The client can contact:
nc 192.168.1.10 9000
For testing UDP:
nc -u -l 9000
The client can send UDP data with:
nc -u 192.168.1.10 9000
Therefore, netcat (nc) is appropriate as a simple netcat network testing utility in troubleshooting communication between two authorised systems.
Netcat For Network Trouble Shooting
You can use netcat (nc) to check if a service is reachable on a certain port. This makes it valuable for debugging Netcat networks.
Say an application should be listening on TCP port 8080. An administrator can try it with:
nc -vz server.example.com 8080
A successful connection means that the destination port is reachable from the testing location. This could be caused by a firewall rule, a routing difficulty, a service failure, the wrong address or some other network problem.
NIST advocates organised network security testing . NIST emphasises testing of systems to discover gaps and improve security controls .
Netcat File Transfer
Netcat (nc) can also be used to show basic file transfer between two authorised computers.
On the system receiving:
nc -l 5000 > received.txt
On the transmitting system:
nc 192.168.1.10 5000 < file.txt
This client-server file-transfer paradigm is documented in the OpenBSD documentation.
However, this method should not be considered a secure alternative to encrypted file-transfer methods. Sensitive data should generally be sent using suitably secure protocols, such as ssh-based solutions.
Two Real-World Examples
Testing a Web Server
A system administrator has deployed a web application on port 8080 but users claim that the application is unreachable.
The administrator performs:
nc -vz 192.168.1.20 8080
If the connection is successful, the administrator knows that the port is reachable from the testing machine. If it doesn’t work, they can look at the web service, firewall, routing or access-control setup.
This way, Netcat (nc) can immediately determine if a problem lies with simple TCP connectivity.
Testing a client server application
A developer writes a test application that is supposed to listen on port 5000.
The developer continues:
nc -l 5000
From another authorised machine they run:
nc 192.168.1.20 5000
The text typed into one terminal is displayed on the other terminal. It gives a quick way to test if the network path and listening port are working before getting into the application problems.
Netcat In Cybersecurity
Netcat (nc) is very related to Netcat cybersecurity activities since it may communicate directly with network services.
Security professionals may leverage it to perform authorised connectivity checks, service testing, network troubleshooting and controlled security assessments. In security labs, Netcat (nc) is also useful to analyse TCP connections, UDP communication, listeners and network sockets.
OWASP’s Web Security Testing Guide also highlights structured security testing, and includes considerations for network architecture and port exposure.
If you are learning Netcat for ethical hacking purposes, do it in an isolated lab environment or on systems you have authorisation to test. Do not try connection or port scanning against unapproved targets.
Netcat Vs Telnet
Netcat ( nc ) vs Telnet Both can be used to create simple TCP connections , however they differ in functionality .
Netcat has more flexibility for scripting, TCP/UDP testing, establishing listeners, testing ports, and rudimentary data-transfer experiments. Telnet was originally intended for interactive communication with a remote terminal.
In terms of fundamental service troubleshooting, Netcat vs Telnet is generally a question of flexibility. Netcat is often more flexible for modern network-testing duties.
Netcat Vs Nmap
Both Netcat (nc) and Nmap can be used to test ports, although for different purposes.
Nmap is a dedicated network discovery and security auditing tool with significant capabilities of scanning and service-detection. Netcat is a little utility for creating connections, listening on ports, transferring data and simple port checks.
So in the case of Netcat vs Nmap it is not just a matter of choosing one tool. Netcat is good for rapid connectivity and service testing whereas Nmap is better suited for full network discovery and scanning.
Security Considerations
Netcat (nc) is strong because it gives you direct network connection. But that versatility means administrators should use it cautiously as well.
Such an untrusted network can present an unwanted attack surface due to an inadvertent exposure of a listener. Firewalls should be configured to block unneeded inbound connections and temporary listeners should be turned off after testing.
According to Microsoft, firewalls can be used to filter traffic based on IP addresses, protocols, and source or destination ports. Google Cloud also suggests least-privilege firewall rules that allow only the traffic, protocols, and ports you require.
Therefore, netcat (nc) should be utilised in controlled contexts, especially when testing for open ports or network services.
Why Is Netcat Called The Swiss Army Knife Of Networking?
Netcat (nc) is often called the Swiss Army Knife of networking because a simple command-line utility may be used to do a wide variety of useful functions.
Netcat client and server, make a Netcat socket connection, test a Netcat open port, send TCP or UDP data, create a Netcat listener, transfer basic files and help with network debugging.
Netcat (nc) is very beneficial for students because the commands show how network connections actually function, without disguising everything behind a graphical interface.
Conclusion
Netcat (nc) is still a useful command line tool to understand and test network traffic. It is useful in networking and cybersecurity with its ability to initiate TCP and UDP connections, listen on ports, test services, transfer data, and troubleshoot connectivity.
Netcat (nc) is very useful for novices since its simple commands show how clients, servers, ports, protocols and sockets connect. At the same time, experienced administrators can use it for quick diagnostics and controlled testing.
Frequently Asked Questions
1. What is Netcat used for?
Netcat ( nc ) TCP and UDP connections , port listening , connectivity testing , simple port scanning , troubleshooting , controlled data-transfer experiments . It is widely used by network administrators, developers, cybersecurity students and security professionals.
2. How to use Netcat on Linux?
You can use netcat (nc) from a Linux terminal with commands like nc host port for connections and nc -l port for listeners. Check your system with man nc or nc -h for the parameters supported, as implementations differ.
3. How to test port using netcat?
For example, you can use netcat (nc) to test a TCP port with the command nc -vz hostname 443. The verbose output may also help to see if the connection attempt is successful or not. Test only systems that you own or have permission to test.
4. Can Netcat be used for file transfer?
Yes. Netcat (nc) can redirect file I/O to transport data between two endpoints. However, simple Netcat transfers do not automatically provide encryption or authentication therefore sensitive files should be transferred using a secure transfer protocol.
5. Is netcat used for ethical hacking?
Yes. Netcat (nc) is used for port testing, interacting with services, debugging networks and understanding how network connections work in authorised security laboratories. Ethical hacking is permission based and with set testing parameters.
Try Our Tools
Netcat (nc) is helpful for learning networking basics, but cybersecurity experts generally need many tools for discovery, analysis, testing and troubleshooting. There is a variety of helpful technology and cybersecurity tools for hands-on learning and testing your network in the Try our tools section at: https://explainmetech.com/tools/
Reference Sources
OpenBSD – Netcat (nc) Manual
OpenBSD nc Manual
OWASP – Web Security Testing Guide
OWASP Web Security Testing Guide
NIST – Guideline on Network Security Testing
NIST Network Security Testing
Microsoft – Windows Firewall Documentation
Microsoft Windows Firewall
NIST – Guidelines on Firewalls and Firewall Policy
NIST Firewall Guidelines
For more helpful technology, cybersecurity, and digital-security tips, visit ExplainMeTech.com and explore our latest guides, tools, and insights.