Administrators log in to Linux workstations, cloud instances, routers, and containers via Secure Shell. It offers direct command-line control, which is why SSH servers are so high on every attacker’s target list. If you put a new server on a public IP address, within minutes people will be trying to connect on port 22 in your logs. The protocol is correct. “The issue is how they set it up.” In this piece, we’ll discuss how hackers exploit misconfigured SSH servers, what settings are important, and how to fix them with commands you can run right now.
What Is SSH Misconfiguration?
An SSH misconfiguration on a server is when the configuration, keys, or network exposure of a server leaves a door open that should be closed. It is not usually a software bug. OpenSSH comes with sensible defaults. The problem is when someone changes them for the sake of convenience in setup and never changes them back.
Some of these practices are password login enabled on all accounts, root login allowed, empty or default passwords, private keys committed to a Git repository, authorized_keys files that no one verifies, and port 22 available to the entire internet. Security misconfiguration is considered A05 in OWASP’s 2021 Top 10. An excellent example is SSH servers. Many SSH servers are created as cloud images that are set up quickly, resulting in temporary shortcuts becoming permanent policies without any documentation. Attackers know the truth. Each day they look for these identical shortcuts over millions of addresses.
Password-Based Vs Key-Based Authentication
Password authentication is the easiest and weakest solution. Anyone who can access the port can attempt to gain entry, and automated tools, which rely on leaked credential lists and common phrases, are designed to perform this type of work. A single account with a password like “welcome123” is all it takes to sell a shell. Even a strong password could be used for other purposes and leaked in another data incident.
Key-based authentication operates differently. You generate a keypair; the public half is on the server, while the private half never leaves your machine. The client proves it has the private key upon login but does not send it. The private key may be safeguarded by a passphrase or hardware token. It’s not possible to guess an Ed25519 key. Keys are not magical, though.
Losing a private key is like losing your house key. Unmanaged keys build up in firms and pose a hidden risk, NIST IR 7966 warns. The practical answer is keys everywhere, passwords off, and a procedure for getting rid of keys that nobody needs any more. Add MultiFactor Authentication to Your Most Sensitive SSH Servers
Root Login Risks
If you set PermitRootLogin=yes, you are giving attackers a head start. All Linux systems have a root account. So they know the username but are missing the password. If they get in, they own the whole system. They can install malware. They can delete logs. They can add backdoor keys. They can read any file.
Shared root access also removes accountability, because the logs say “root” and you can’t determine which human did what. The safer approach is to have a named account that uses sudo for the few times you need privilege. Disabling PermitRootLogin is a cost-effective measure that secures one of the most frequently targeted entry points on SSH servers globally.
Common SSH Attacks
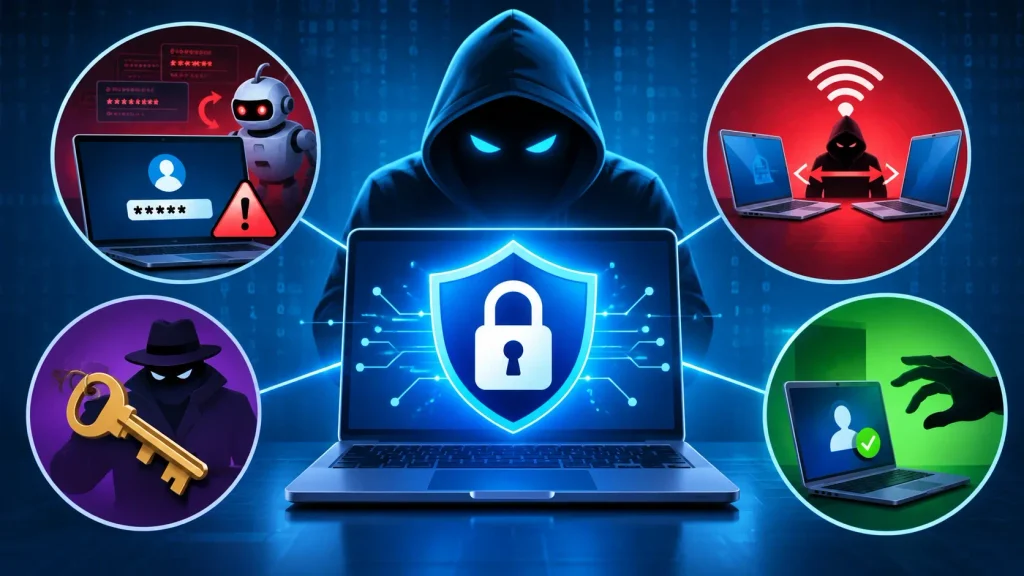
Brute force and credential stuffing are the most common attacks. Bots don’t get tired, and they will try thousands of usernames and passwords. This method is also how a breach on some unrelated website might become a shell on your machine: compromised passwords are replayed against many SSH servers simultaneously.
Stolen or leaked keys are more low-profile. Occasionally a developer will accidentally check a private key into a public repo or leave an unprotected copy on a shared box. Then that key can be used to log in with no failed attempts whatsoever. Another related technique is persistence. Once an attacker gets in, he adds his own public key to authorized_keys so that he can return later, even if the password is reset.
Other attacks target either the link or the application. If a user dismisses a host key warning, a man-in-the-middle can place himself between the client and the server and steal credentials. In July 2024, Qualys published regression (CVE-2024-6387), a race condition in OpenSSH’s sshd that allowed unauthenticated remote code execution on vulnerable glibc-based Linux systems. Unpatched machines remained vulnerable until they upgraded.
Loose forwarding settings also carry risk, as a compromised server might be used as a tunnel into internal networks. Most of these channels are closed on SSH servers by patching, cleanliness, and rigorous sshd_config rules.
Real Examples
Operation Windigo and the Ebury Backdoor
In 2014 ESET researchers wrote a paper detailing Operation Windigo, a campaign that attacked more than 25,000 Linux and Unix computers for a period of around two years. At its center was Ebury, a nasty OpenSSH backdoor that quietly stole the credentials of anyone logging in.
The credentials were utilized in other attacks, and the hacked workstations were used to send out spam and send visitors to malicious URLs. The point is simple: without monitoring the SSH layer, one captured admin login can spread to numerous SSH servers. Checking the integrity of the sshd binary, looking for odd outgoing traffic, and safeguarding keys with passphrases make the work substantially harder for the operators.
The SSH-Snake Worm
In January 2024, the Sysdig Threat Research Team released details on SSH-Snake, a self-replicating program that propagates across a network via SSH credentials discovered on a compromised machine. It looks for private keys in the .ssh folder, shell history, and known_hosts, logs in to the next host, and repeats the process. Sysdig says it has witnessed real threat actors utilizing it. The hole it uses is not an OpenSSH bug. It’s a collection of habits: private keys with no passphrase, one key trusted on many machines, and years of stale entries nobody cleaned up. Loose trust between SSH servers turns one compromised laptop into a network-wide problem.
SSH Hardening Commands
Make sure you can connect with key authentication. Start on your own computer: create a modern key pair, copy the public key to the server, test the login. Do not modify anything else. Keep one session active while you edit, so a typo can’t lock you out, and try it on a test computer before touching production ssh servers.
Bash
ssh-keygen -t ed25519 -C “admin@example.com”
ssh-copy-id user@your-server-ip
Auto
Then enter /etc/ssh/sshd_config and set below values. If you need port forwarding for a certain user, simply enable it in a Match block for that account.
- PermitRootLogin no
- PasswordAuthentication no
- PubkeyAuthentication yes
- PermitEmptyPasswords no
- MaxAuthTries 3
- LoginGraceTime 30
- AllowUsers deploy admin
- X11Forwarding no
- AllowTcpForwarding no
- ClientAliveInterval 300
- ClientAliveCountMax 2
Check the file for errors and reload the service. On Debian and Ubuntu it is named ssh, on the RHEL-family it is sshd.
Bash
sudo sshd -t && sudo systemctl reload ssh
Then restrict who can hit port 22 and add auto bans for repeated failures. * Replace the sample address with your own admin IP address.
Bash
sudo ufw allow from 203.0.113.10 to any port 22 proto tcp
sudo ufw enable
sudo apt install fail2ban -y
sudo systemctl enable –now fail2ban
Lastly, check the live settings and recent failures. Do this on each of your SSH servers, not just the primary one.
Bash
sudo sshd -T | grep -Ei “permitrootlogin|passwordauthentication”
sudo grep “Failed password” /var/log/auth.log | tail -n 20
Best Practices For SSH Security
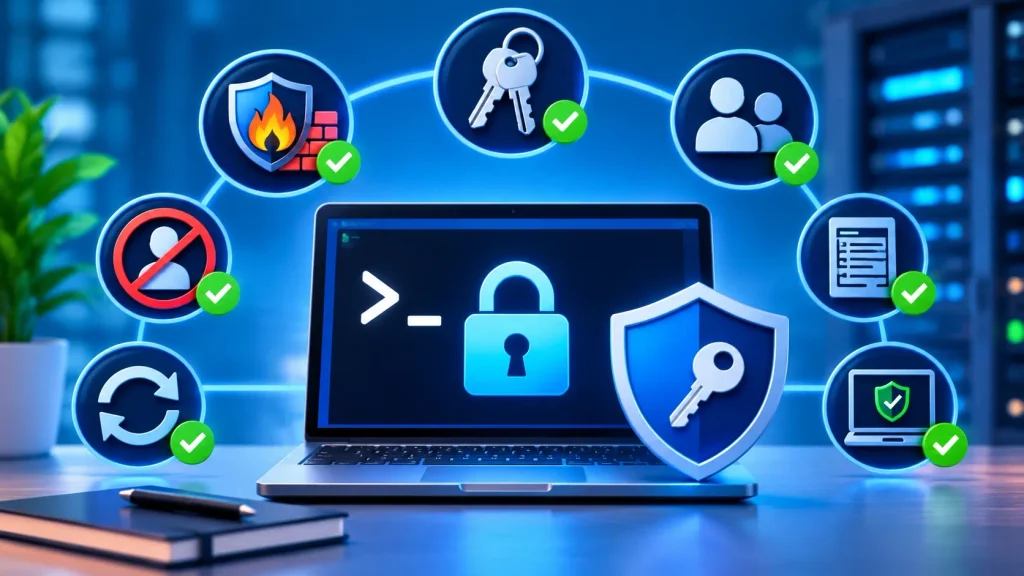
Hardening is not a one-time job. Keep OpenSSH patched—issues like regression only affect unpatched devices. Use hardware-backed keys (ed25519-sk) or multi-factor authentication for admin accounts. SSH servers should not be accessible to the internet but be behind a VPN or a bastion host. Use your cloud service to provide a central identity: Google Cloud OS login links SSH access to IAM roles. Microsoft adds OpenSSH support and Entra ID sign-in to Azure Linux VMs.
Create a different key for each person and each function. Remove keys when people leave. Audit authorized_keys every 3 months. Log failed logins. Log new keys. Set alerts for both. Run the open-source SSH-audit tool against your SSH servers regularly to identify broken algorithms. Do not paste private keys into conversation or commit them to a repository. It also reduces log noise by changing the port from 22 but is not a protection in itself.
Conclusion
SSH is seldom compromised by attackers. They walk in through doors administrators leave open: password logins, root access, lost keys, unpatched software. The fix is not difficult. Use key-based authentication, disable root and password login, limit access to port 22, maintain OpenSSH up to date, and examine keys and logs periodically. Both Windigo and SSH-Snake demonstrated that a single compromised credential can spread throughout a network. Spend an hour today protecting your systems and you remove the easiest path for the attackers.
Frequently Asked Questions
1. SSH misconfiguration explained simply?
The attackers are abusing a weak or careless configuration of the SSH service (e.g., allowing passwords or enabling root login). Hardened SSH servers plug those holes.
2. Is changing the default SSH port safe enough?
No. A new port only hides your SSH servers from the lazy scanner. You still need keys, patching, and firewall restrictions. Any determined attacker will find it.
3. Must I stop password authentication?
Yes, when you have tested, your key logins work. Disable Passwords: To remove passwords as an attack vector for your SSH servers, you need to disable them.
4. How can I tell if my SSH servers were attacked?
Look through /var/log/auth.log (or journalctl -u ssh) for failed and unexpected successful logins. Run the final command, and scan the authorized_keys file for any keys that you don’t recognize.
5. Can Fail2Ban substitute for hardening?
No, fail2ban stops repetitive guessing, but it can’t fix an open root login or a leaking key. Use it as an overlay over others.
Try Our Tools
Feel like trying your own setup? Try our ExplainMeTech Tools. Our free browser-based tools enable you to test, evaluate, and harden the basics of your digital security so you can detect weak spots on your SSH servers before an attacker does.
References
- OWASP. “A05:2021 – Security Misconfiguration.” OWASP Top 10:2021. owasp.org/Top10/A05_2021-Security_Misconfiguration
- NIST. “NIST IR 7966: Security of Interactive and Automated Access Management Using Secure Shell (SSH).” csrc.nist.gov/pubs/ir/7966/final
- Microsoft Learn. “OpenSSH for Windows overview.” learn.microsoft.com
- Google Cloud. “About OS Login.” cloud.google.com/compute/docs/oslogin
- OpenBSD. “sshd_config(5) manual page.” man.openbsd.org/sshd_config
If you want more technology, cybersecurity and digital-security ideas, head on over to ExplainMeTech.com and see our latest guides, tools and insights.