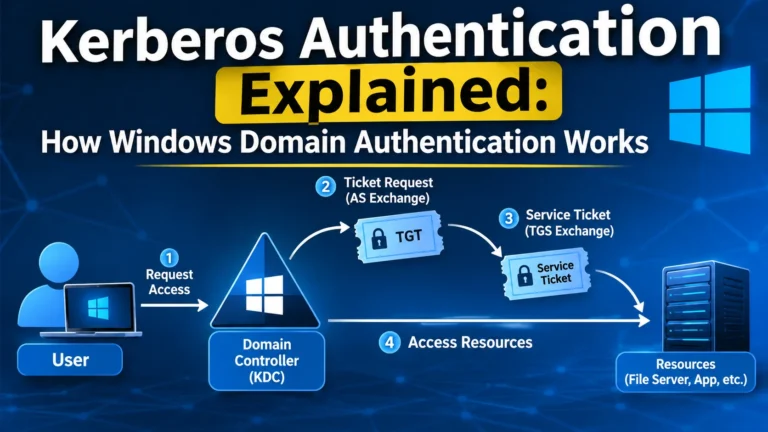
Millions of individuals sit down every day, type a password once, and then open file shares, intranet sites, email and databases without being asked to sign in again. In most Windows settings, Kerberos authentication is the silent engine performing that...
Every modern app talks to something else: a database, a payment gateway, a cloud storage bucket, an email service. Each of those discussions requires confirmation of identification, and that proof is hidden. Secrets Management is the art of keeping those...
We mostly know about websites dropping cookies to remember us. Many of us also know how to delete those cookies in a few clicks. What fewer people understand is that a site may often identify a recurring visitor without storing...
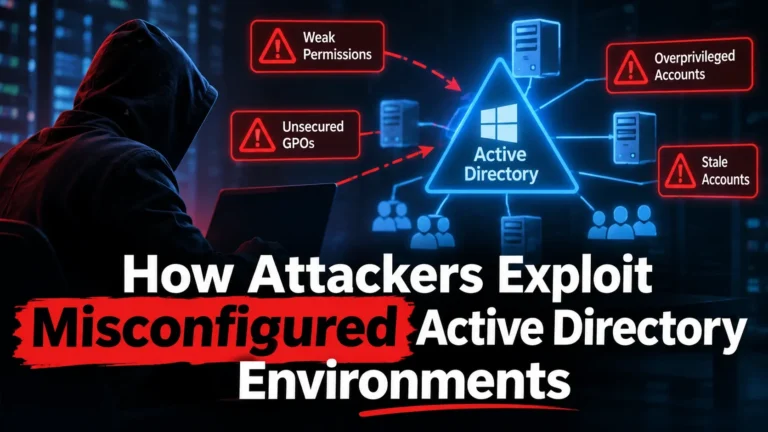
Most ransomware cases have the same ending: someone takes over a domain controller. Active Directory Environments are the backbone of practically every Windows network. When mishandled, one weak password can lead to a company-wide compromise. In this post, we’ll show...

Software Supply Chain Attacks: Most firms spend their security dollars defending the front door: firewalls, phishing training, endpoint technologies. The attackers noticed and several of them stopped knocking. Instead, they sneak inside the software you already trust and let you...
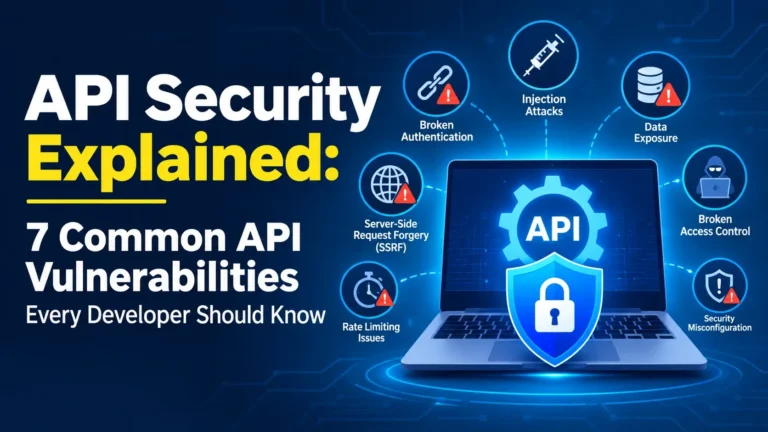
Every program on your phone speaks to a server using an API: your bank balance, the live location of your cab, even the weather widget on your home screen. And that convenience is why API security is a major worry...

A single wrong header can expose your users’ private info to a random stranger. That is the true hazard of a CORS Misconfiguration. Nothing is broken, no alarm is sounded, and the application continues to perform just as it did...
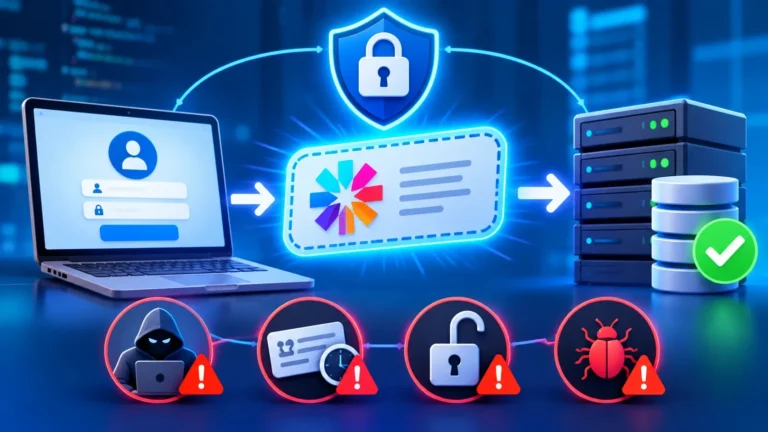
If you have constructed a login system in the last couple of years, you have almost likely come across JWT Authentication. Behind single page apps, mobile backends, microservices, and even the “Sign in with Google” button sits . The premise...
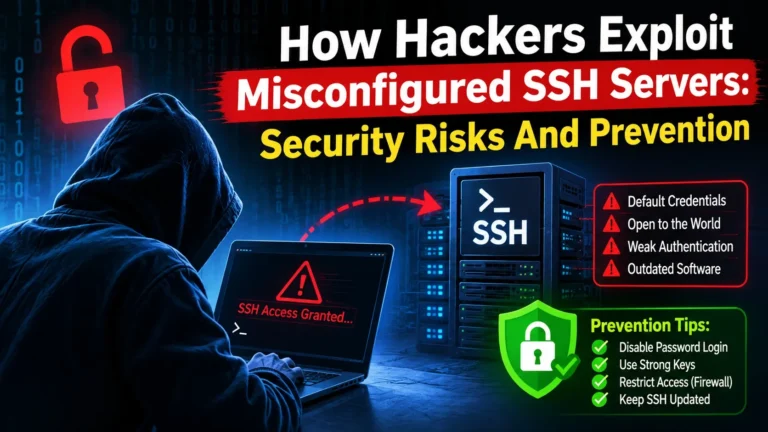
Administrators log in to Linux workstations, cloud instances, routers, and containers via Secure Shell. It offers direct command-line control, which is why SSH servers are so high on every attacker’s target list. If you put a new server on a...