We mostly know about websites dropping cookies to remember us. Many of us also know how to delete those cookies in a few clicks. What fewer people understand is that a site may often identify a recurring visitor without storing anything on the device at all. That subtle technique is known as browser fingerprinting and has become one of the most debated topics in web privacy and security. In this book, you’ll discover how it works, why companies rely on it, what hazards it poses, and what you can actually do about it.
What Is Browser Fingerprinting?
Browser fingerprinting is when lots of little details about your browser and device are collected and then combined into one identity. No one fact gives you away. Millions of people have your time zone, millions of people have your browser version. But when a script reads dozens of these numbers in combination, the combination may be unusual enough to lead back to a single machine. Imagine describing a stranger in a crowd. “tall” describes thousands, while “tall, red coat, slight limp, carrying a violin” describes absolutely nobody.
Unlike a cookie, nothing is kept on your computer. All the site has to do is recalculate the identification every time you come back . Clearing your history scarcely slows it down . You might also see it dubbed device fingerprinting or cookieless tracking. The notion has been investigated by researchers at least since 2010.
How Websites Collect Browser And Device Information?
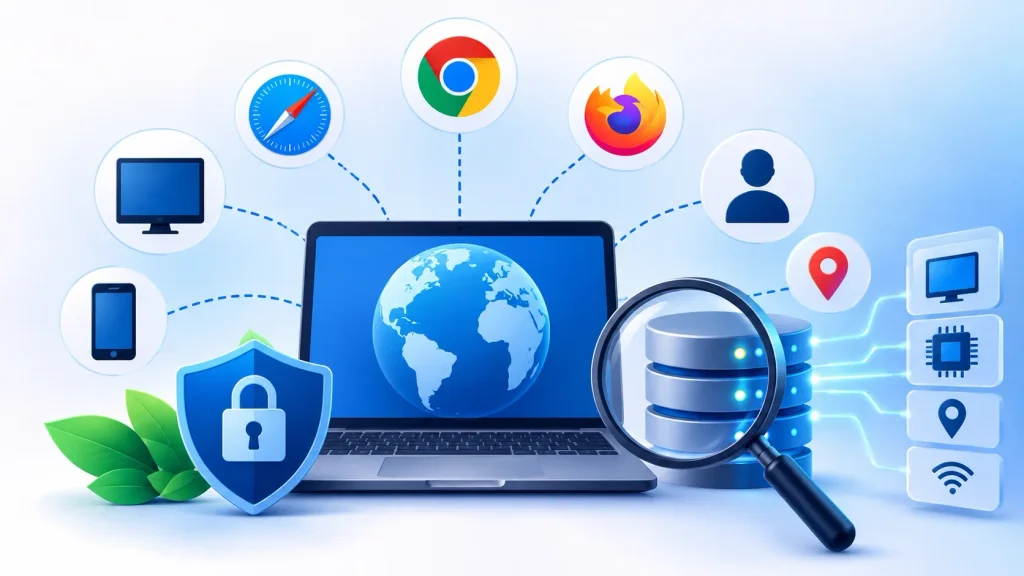
A fingerprinting script is often just a few lines of JavaScript code that runs when a page loads. It asks enquiries of your browser through the same web APIs developers use to make pages responsive and accessible. The browser replies truthfully, as it has no reason to question the request. The script takes the responses , concatenates them , and runs the concatenated string through a hash function to get a short ID . Some details also come in passively, inside the HTTP headers your browser provides with each request, so a server can read them without running any code at all. That mix of active and passive collection is exactly what makes browser fingerprinting so hard to detect.
The Role Of IP Address, Screen Resolution, Fonts And Browser Settings
“The most obvious signal is your IP address. It provides your network provider and rough location. On its own, it is poor (many homes share one address, and mobile providers rotate them), but a helpful supporting hint. Your display is described by screen resolution, colour depth, and pixel ratio. The list of installed fonts is surprisingly informative, as it is dependent on your operating system, language packs and software such as design tools or office suites.
The user agent string tells your browser and operating system. Add language, time zone, number of CPU cores, device RAM, touch support, cookie or Do Not Track settings, and much more detail. Security specialists call this detail entropy: How much does a value assist narrow down who you are? “Each setting adds a little and all together, they add up to a lot.”
Canvas And WebGL Fingerprinting
Canvas fingerprinting is when you ask your browser to draw a concealed image, usually a line of text with colours and shapes, using the HTML5 canvas element. You never saw the film. The script simply reads the pixels back and hashes them. The pixels are slightly different from one machine to the next due to small changes in graphics drivers, font rendering and anti-aliasing, so is the hash. WebGL fingerprinting takes it a step further. WebGL lets a page render 3D visuals and can reveal the GPU vendor, renderer name and available extensions.
Another stable value is obtained by rendering a hidden 3D scene and hashing the result. Audio fingerprinting is the same thing, except with a sound signal no one can hear. These tests are important because they are based on hardware and driver behaviour that is more harder to modify than a setting. They’re also the reason why browser fingerprinting is so hard to ban without affecting genuine websites, and why they’re at the basis of modern browser fingerprinting kits.
Browser Fingerprinting In Practice: Two Browsers On One Device
Think about a single laptop with both Chrome and Firefox on it. You’d expect to see the same visitor twice on a website. It’s actually looking at two separate fingerprints that overlap a lot . The table shows why, with illustrative rather than actual values.
| Signal | Chrome (Blink engine) | Firefox (Gecko engine) | Same? |
| IP address | 203.0.113.25 | 203.0.113.25 | Yes |
| Screen resolution | 1920×1080 | 1920×1080 | Yes |
| Time zone | Asia/Kolkata | Asia/Kolkata | Yes |
| User agent | Chrome on Windows | Firefox on Windows | No |
| Canvas hash | 9f3a41… | c71d08… | No |
| WebGL renderer string | Full GPU name | Often generalised | No |
| Final fingerprint ID | A91F-22C0 | 7C2E-5B14 | No |
The two IDs are different because each browser has a distinct rendering engine, produces text and graphics differently, and reports a different user agent. And this is how a site turns that into acknowledgement. On your initial visit it keeps the ID beside a session or account record. On the next visit it re-calculates the ID and checks for a match. But real systems don’t usually require a perfect match .
Browsers get updated , and people install new fonts . So they score how similar two fingerprints are , and accept a close call . Shared signals (IP address, screen, time zone, GPU) can also allow an analyst to estimate that both browsers belong to the same individual. This is how browser fingerprinting catches visitors who switch browsers to escape tracking.
How Browser Fingerprinting Is Used For Tracking And Fraud Detection?
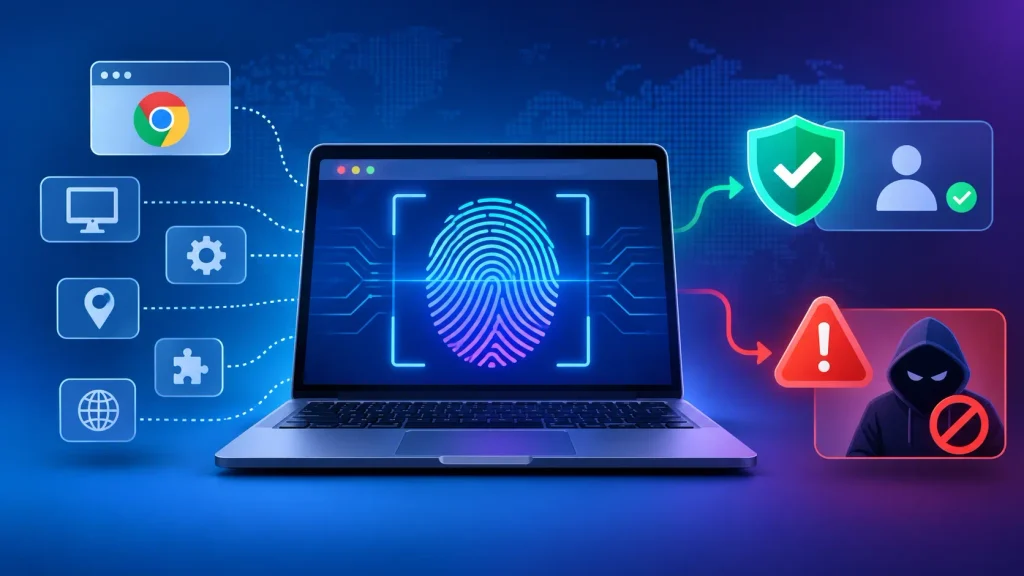
Advertisers and analytics companies use fingerprints to identify visitors across sessions, and occasionally across sites, when cookies are blocked or removed. That’s the tracking part, and that’s the part privacy activists are concerned about. There’s a defensive side too. Banks, online merchants, ticket sellers and payment processors employ browser fingerprinting to assess the risk.
In the event that an account that usually signs in from one device suddenly appears on a fingerprint no one has seen before, the site can seek more verification. The same data helps uncover bots, false sign ups, card testing, one person running dozens of accounts. The dual usage is why the approach is hard to ban outright: the code that follows you around for adverts is almost identical to the code that stops a stranger emptying your account.
Two Real-World Examples
The EFF Panopticlick study (2010)
The Electronic Frontier Foundation asked visitors to test their browsers and evaluated around 470,000 of them. It found 83.6 percent had a completely unique fingerprint, and more so, 94.2 percent, among browsers with Flash or Java enabled. The result: browser fingerprinting works on totally conventional settings, without hacking.
The Web Never Forgets” (2014)
Researchers from KU Leuven and Princeton crawled the top 100,000 websites and found that about five percent of them contained scripts for canvas fingerprinting, most of which came from a third-party widget firm called AddThis. AddThis indicated that it ceased utilising the technique after the findings were released. It was an early public demonstration that browser fingerprinting was already being executed at scale on real sites.
Privacy Risks And Security Concerns
The big problem is permission. At least a cookie banner gives you an option. Browser fingerprinting happens in the background, and there is nothing you can delete. It’s also persistent: the identification can remain steady for weeks or months, and can link your activity across unrelated sites. Profiles constructed this way can give hints about sensitive issues such as your language, interests, work environment or even the age of your hardware. European regulators have said that consent regulations can apply to this form of tracking, but enforcement is patchy.
Security issues go the opposite way, too. Hackers find databases of stored fingerprints an interesting target. The attackers can copy or fake a victim’s values, to get past the fraud checks. Tools that do exactly that are marketed on criminal marketplaces . Fingerprint-based choices might sometimes go wrong: a tourist on a new phone, or someone using a privacy-focused browser, might be mistakenly marked as suspicious. So browser fingerprinting should be one signal among many, not proof of identification. That’s consistent with the layered, risk-based reasoning in NIST’s digital identity standards.
How To Reduce Browser Fingerprinting?
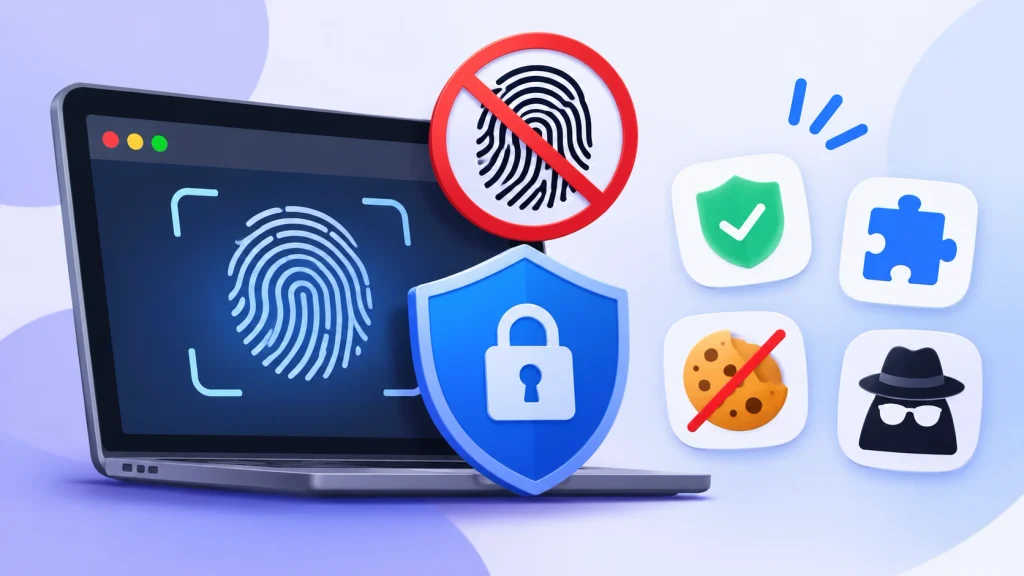
You can’t get rid of your fingerprint, but you can make it less unique. The aim is to merge with a crowd, not to hide from it.
Choose a protective browser: Select a browser with built-in protections against browser fingerprinting. Firefox prevents known fingerprinting scripts Enhanced Tracking Protection: Brave introduces modest random alterations to canvas and audio output . Tor Browser makes all its users seem alike .
Keep everything updated: Patched browsers and drivers return common values. This helps you blend in.
Go easy on extensions and tweaks: Each uncommon add-on, typeface or setting adds entropy, and certain anti-tracking add-ons make you stick out more than they hide you.
Separate your profiles: Maintain different browser profiles for work, banking and casual surfing so one identity doesn’t follow you everywhere.
Test yourself: The EFF’s Cover Your Tracks tool demonstrates your vulnerability to browser fingerprinting—and whether your browser blocks it.
Know what doesn’t help: A VPN only changes your IP address, and private or incognito mode only prevents local history, so neither changes your canvas, fonts or hardware signals.
Final Thoughts
Browser fingerprinting is here to stay, as the same method that enables tracking also helps safeguard accounts from fraud. The practical approach is transparency and restraint: sites should tell users what they gather, and use information only for defined goals, and users should use browsers that limit the damage. First, to control the system, you must know how it operates.
Frequently Asked Questions
1. Is fingerprinting legal?
Depends on where you are and how you want to use the data. Regulators in the EU have suggested that permission regulations such as the ePrivacy Directive can be used, and the GDPR applies to fingerprints that can be used to identify a person. Fraud prevention usually gets less attention. The information provided is of a general nature and is not intended to be legal advice.
2. Will incognito mode stop browser fingerprinting?
No. Incognito mode just prohibits your browser from keeping history and cookies locally. Your screen, fonts, GPU and settings seem identical, thus a script can still compute almost the same fingerprint.
3. Can a VPN prevent fingerprinting?
Only partially. A VPN can hide your IP address, but that’s just one of many signals. Canvas , WebGL , fonts , language , and hardware data are untouched so websites can still tell your device apart .
4. How reliable is browser fingerprinting?
It depends. Early studies found that most browsers were unique, but later study on millions of visits discovered considerably less unique fingerprints, especially on phones. Fingerprints also wander with software changes, therefore sites combine it with other signals.
5. How can I check my fingerprint?
In each of your web browsers, open the EFF’s Cover Your Tracks. You can easily see what browser fingerprinting says about you, how unique your configuration looks and if the browser is blocking tracking scripts.
Try Our Tools
Curious about what your own browser leaks? Try our tools at ExplainMeTech Tools Page and see a growing collection made to make browser fingerprinting, online privacy and other digital-security problems easier to comprehend and act on.
References
- OWASP. Web Security Testing Guide. Testing and information-gathering guidance that covers how fingerprinting techniques reveal technology details.
- NIST. SP 800-63-4, Digital Identity Guidelines. Federal guidance on identity assurance and authentication, including risk-based thinking.
- Microsoft. Tracking prevention in Microsoft Edge. How Edge limits cross-site trackers.
- Google. Privacy Sandbox overview. Google’s stated approach to reducing cross-site tracking on the web.
- Laperdrix, Bielova, Baudry and Avoine. Browser Fingerprinting: A survey. Academic overview of techniques, studies and defences; it also summarises both studies cited in the real-world examples (EFF Panopticlick, 2010, and “The Web Never Forgets”, 2014).
If you want more technology, cybersecurity and digital-security ideas, head on over to ExplainMeTech.com and see our latest guides, tools and insights.