Most ransomware cases have the same ending: someone takes over a domain controller. Active Directory Environments are the backbone of practically every Windows network. When mishandled, one weak password can lead to a company-wide compromise. In this post, we’ll show through how attackers actually accomplish it—from the initial glance around to full domain takeover—and what you can do to lock the door. It’s written to give admins, students and security teams the practical picture without the jargon.
What Is Active Directory (AD)?
Active Directory is a directory service from Microsoft. It holds users, machines, groups and rules and it selects who can log in to what. When an employee logs onto a laptop in the morning, a domain controller verifies their identity and hands back a ticket that demonstrates it. That’s the short explanation of how Active Directory Environments operate the daily life of a corporation.
The problem is that AD was built for convenience in an era where the network perimeter was trusted. Any authenticated user can read large volumes of directory data by default This is by design and is exactly why Active Directory Environments are such a favourite target. If you own the directory, you control the business.
How Attackers Enumerate Active Directory Environments?
Enumeration is the mapping process and is where attacks on Active Directory Environments start. Once the attacker gets onto one workstation — generally via phishing or a stolen VPN login — they start asking the directory questions. Who is the Domain Admins Which accounts have SPNs? The following machines allow unbounded delegation: Which groups nest in other groups?
Normal domain users can query LDAP, therefore none of this needs special rights. Attackers employ built-in Windows commands and open-source graph tools to create a visual trail from “ordinary user” to “Domain Admin” out of thousands of relationships. The defenders also employ the same graph techniques to locate those paths first, and it is worth knowing that. The whole phase happens quietly in poorly monitored Active Directory Environments, as nobody is checking for bursts of LDAP queries coming from a random workstation.
Common Misconfigurations In Active Directory Environments

Attackers targeting Active Directory Environments rarely need a zero day. They depend on settings that have never been examined. The usual suspects look something like this:
Service accounts with weak, outdated or non-expiring passwords.
Too many people in Domain Admins or other high-privilege groups.
Accounts that have “Do not require Kerberos preauthentication” enabled.
Unrestricted delegation on servers that do not require it.
Common local administrator passwords on all workstations.
Too permissive permissions on objects Groups and Group Policy Legacy protocols such as NTLMv1 and SMBv1 still allowed Certificate templates that allowed low privileged users to request powerful certificates
Any one of these is doable. There is risk in the mix. The same scenario plays out in many Active Directory Environments. A neglected service account, a recycled password, and a privileged group that hasn’t been audited in years.
Kerberoasting And ASREP Roasting
Kerberoasting exploits the way Kerberos works. A service account has a service principal name , and any domain user can request a service ticket for it . That ticket is partially encrypted using a key obtained from the service account password. The attacker takes the ticket off line and guesses passwords at his leisure, without any unsuccessful logins and without lockouts to set out an alarm. A short or predictable password can be cracked in minutes. If it is a long random string the attack goes nowhere.
The sibling is AS-REP Roasting. If an account has Kerberos preauthentication disabled, anyone can request a response encrypted with that user ‘s password-derived key, without knowing the password. Same crack offline, same result. The reason these attacks succeed is because to bad passwords and outdated configurations, not a vulnerability in the program. This is why so many Active Directory Environments stay vulnerable for years.
Pass-The-Hash Attack
Inside Active Directory environments, Windows can authenticate with a password hash instead of the password itself using NTLM. If an attacker takes that hash from memory on a compromised machine they can provide it directly and log in elsewhere. They don’t have to break it up.
The true damage is in the reuse. One stolen hash is enough to open all the laptops if they all have the same local administrator password. If a domain admin ever logs in to a compromised server, their credentials could be sitting in memory for the attacker to obtain. This lateral movement is how a single infected workstation becomes hundreds in current Active Directory Environments.
How Privilege Escalation Happens?
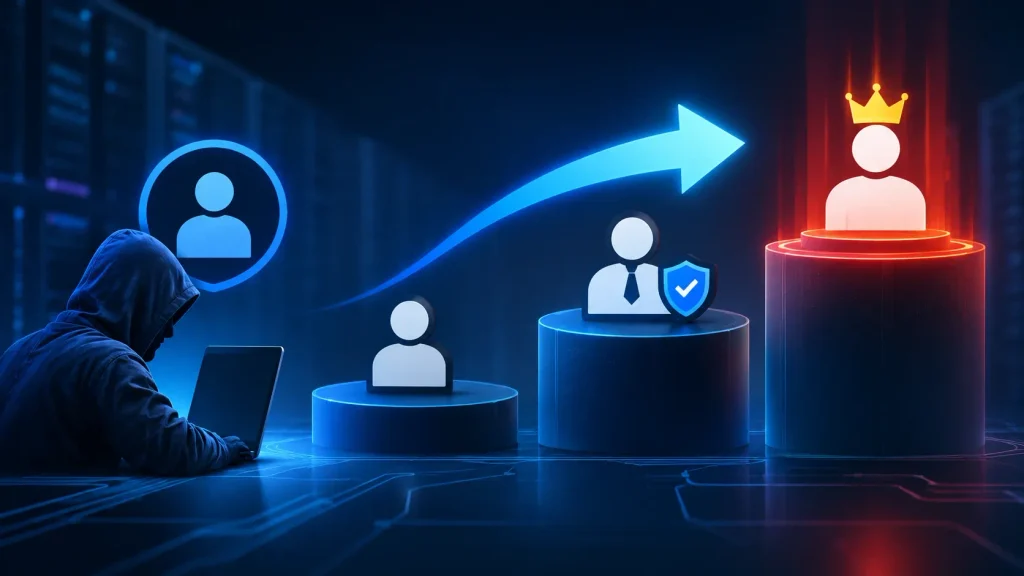
Privilege escalation in Active Directory Environments is typically a series of little steps, not a single large jump. A typical path is the following. The attacker begins as a regular user, cracks a service account, and learns that account is a local admin on a few systems. One of those servers has an active session for a more privileged user. The attacker takes those credentials and that account has write access to a group that controls a domain administrator. A few hops later they possess the domain
Other attack paths are delegation abuse, incorrect certificate templates, and permissions such as GenericAll or WriteDacl on sensitive objects. Once the attacker can reproduce directory data or reset the secret trust of the krbtgt account, they can fake tickets that live well past when the initial breach has been “cleaned up.” And that’s where healing really starts to hurt.
Practical Scenario: Weak Service Account Passwords Plus Excessive Privileges
Imagine a mid-sized firm. A finance employee clicks a phishing link and the attacker gets a normal user session. A quick search of the directory shows a service account called svc-backup with a service principal name.
They ask for its ticket and break it off the queue. The account was created years ago and nobody has ever used it since. The password is “Backup2019!” That’s error number one: a weak password on a service account that never expires.
The second error is more egregious. Someone added svc-backup to Domain Admins “for ease of backups”. The attacker now gets on with full domain permissions, copies the directory database from a domain controller, and finds himself in possession of every password hash in the firm. It’s ransomware deployed overnight. One bad password and one excessive permission leaked the entire domain. That’s how fast poorly managed Active Directory Environments get compromised.
Two Real-World Examples
NotPetya (2017)
The NotPetya outbreak devastated global corporations like shipping giant Maersk. It spread by stealing credentials from memory and reusing them on machines in a pass-the-hash manner of lateral movement at scale. Maersk later said it lost over $300 million. The business had to replace thousands of servers and tens of thousands of PCs. The only domain controller that survived was said to be in an office which lost power during the attack. It demonstrates the effect of poor credential hygiene and segmentation in big Active Directory Environments.
SolarWinds (2020)
In the SolarWinds supply chain hack, the intruders didn’t just stop at the compromised software. Once inside, the attackers targeted identity infrastructure, gaining administrative access and forging authentication credentials to contact cloud services as legitimate users, CISA and Microsoft explained. The lesson is the identity layer is the actual prize and on-premises Active Directory Environments are just as important to defend as the cloud.
Best Practices To Secure Active Directory Environments
Active Directory environments are largely about eliminating simple pathways . You may begin today . Try these first:
Use group Managed Service Accounts (gMSA): These have long passwords that are automatically rotated, making Kerberoasting problematic. For accounts that cannot use gMSA, passwords must be at least 25 characters long.
Apply least privilege: Domain Admins should be nearly empty. Have separate admin accounts and never use them for email or surfing.
Use a tiered administration model: Never log on to workstations or regular servers with the domain admin credentials.
Deploy Windows LAPS: Unique local admin passwords that rotate means one hash doesn’t open up every machine.
Enforce strong authentication: Disable preauthentication exceptions, decommission NTLMv1 and SMBv1, enable SMB signing and enable LDAP signing.
Audit regularly: Check delegation, group nesting, ACLs and certificate templates. Do your own attack-path analysis on your own network before someone else does.
Monitor and log: Alert on anomalous Kerberos ticket requests, new members of privileged groups, and directory replication from non-domain-controller hosts.
Protect the krbtgt account: Rotate the secret on schedule and after any suspected compromise, then rotate a second time after the first rotation.
Back up and rehearse recovery: Have offline, tested backups of your domain controllers and know how to recover your forest before you need to.
None of this is exotic: Teams that implement these fundamentals properly make their Active Directory Environments substantially more difficult to take over.
Conclusion
Attackers don’t hack Active Directory Environments the way they do in the movies. They walk in through weak service account passwords and forgotten rights and settings that no one evaluated. Managing one domain or multiple domains, Active Directory Environments benefit from frequent upkeep. Fix those shortcomings, keep a tight check on the directory and one click on a phishing email will no longer mean the end of the organization.
Frequently Asked Questions
1.What is the most prevalent method attackers use to exploit Active Directory Environments?
The most prevalent method is stolen or weak credentials, usually followed by abuse of misconfigurations such over-privileged service accounts. Attackers seldom need an exploit when a password would do.
2. How is Kerberoasting different from AS-REP Roasting ?
Kerberoasting is where you target service accounts by requesting service tickets and cracking those tickets offline. AS-REP Roasting attacks accounts whose Kerberos preauthentication is disabled. Both rely on offline password-guessing.
3. Is it possible to prevent Pass-the-Hash?
Not with one setting but you may make it really hard. Use LAPS for unique local admin passwords, tiered administration, Credential Guard, restrict NTLM and keep privileged logins off of normal PCs and stolen hashes that can’t travel far.
4. How often should I audit Active Directory Environments?
Automate checks on a continual or at least monthly basis. Perform a more thorough examination of privileged groups, delegation and permissions every quarter. Audit also after mergers, big migrations or any security issue.
5. Are gMSAs enough to prevent Kerberos credential theft?
They eliminate much of the risk because their passwords are long, random and rotated automatically. You still have to deal with old service accounts, clean up unneeded SPNs and watch out for fraudulent ticket requests.
Try Our Tools
Looking to implement these ideas? Check out the free utilities at ExplainMeTech Tools page and discover security and technology helpers that help to make checking, learning and hardening Active Directory Environments a little easier.
References
- OWASP, Top 10: A05 Security Misconfiguration and A07 Identification and Authentication Failures: https://owasp.org/Top10/
- NIST, SP 800-63B Digital Identity Guidelines (Authentication and Lifecycle Management): https://pages.nist.gov/800-63-3/sp800-63b.html
- Microsoft Learn, Best Practices for Securing Active Directory: https://learn.microsoft.com/en-us/windows-server/identity/ad-ds/plan/security-best-practices/best-practices-for-securing-active-directory
- Microsoft Learn, Group Managed Service Accounts Overview: https://learn.microsoft.com/en-us/windows-server/security/group-managed-service-accounts/group-managed-service-accounts-overview
- Google Cloud / Mandiant, M-Trends Report: https://cloud.google.com/security/resources/m-trends
If you want more technology, cybersecurity and digital-security ideas, head on over to ExplainMeTech.com and see our latest guides, tools and insights.